CEO Threats Are Rising: When Online Warning Signs Point to Real-World Risk
CEO threats are rising rapidly. In 2025, reported incidents targeting senior private-sector executives had already doubled from the year before. CEOs were the target in 64 percent of cases. One in three incidents resulted in death or physical injury.
Online rhetoric calling for violence against CEOs is also rising. From late 2025 to early 2026, it increased nearly fivefold, according to Security Today.
Some of the warning signs are hiding in plain sight. A recent social media graphic featuring Flock Safety CEO Garrett Langley showed his photograph beside three bullets and the words “NO CEO LEFT BEHIND.”
The caption read, “Let’s downsize.”

The post has since been taken down, but CEO threats and similar posts targeting executives remain visible on the same account.
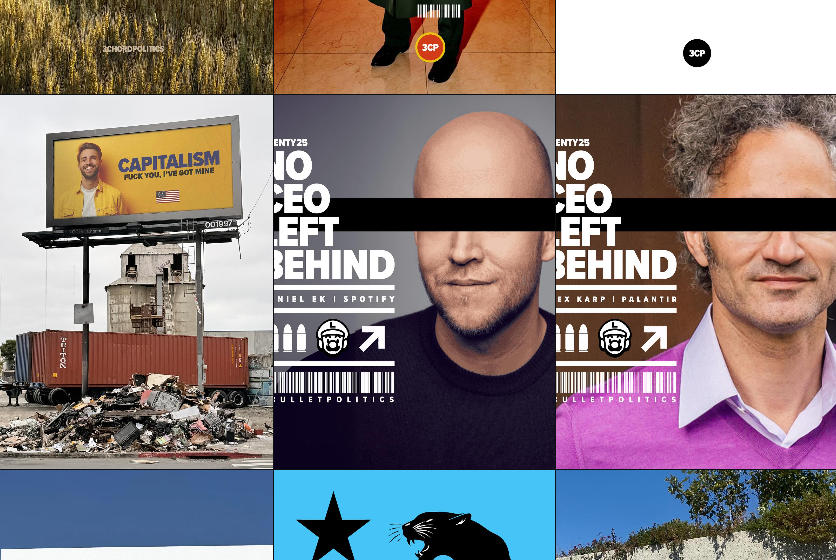
Criticism comes with being a public leader. Violent imagery directed at a named CEO raises a different question: How seriously should it be taken?
That question carries more weight following the December 2024 killing of UnitedHealthcare CEO Brian Thompson.
In the roughly five weeks after his death, Nisos identified more than 2,200 online threats against executives. In the six months before the killing, researchers had identified more than 1,560 direct threats against CEOs. They also began seeing variations of Luigi Mangione’s name used as coded language in threatening posts.
The warning signs are online. So is much of the information someone would need to locate an executive, understand their routines, or expose their family.
That is why modern executive protection increasingly starts online.
When Does Online Threats Against Executives Become a Real Security Concern?
A single hostile post does not establish that an executive is in physical danger. Concerns increase when it becomes part of a larger pattern of violent language, fixation, preparation, personal information gathering, or attempts to get closer to the target.
People say ugly things online every day. Most angry posts never lead to physical violence. The challenge is knowing which ones warrant a closer look.
The FBI's behavioral threat guidance emphasizes patterns and escalation. Security teams pay closer attention when they observe violent intent becoming more specific, a repeated fixation on a person, efforts to gather information about the target, attempts to understand security, or signs of preparation.
For a CEO or the team protecting one, that means looking beyond a screenshot:
Is one person becoming increasingly fixated on the executive?
Is the language becoming more specific or more violent?
Are they gathering or sharing information about the executive, family, home, travel, or schedule?
Are they trying to make contact, approach the executive, or understand how the executive is protected?
One post may not answer any of those questions. It may give you a reason to start asking them.
Taking a concerning signal seriously does not require predicting what someone will do next. It requires sufficient visibility and judgment to recognize when the pattern has changed.

Would Your Organization Know If Someone Was Threatening Your CEO Online?
Many organizations already have pieces of the capability to detect an online threat. The vulnerability is often that no one owns the full picture.
Would your organization know? If so, who would know first? Who is actually monitoring threats against your executives?
Is the same team monitoring social media also reviewing threat intelligence, data leaks, doxxing, or activity outside the major platforms? How often is that information reviewed?
If your organization has separate cybersecurity, physical security, intelligence, communications, or executive protection functions, do they regularly bring what they are seeing?
When one team spots something concerning, is there a clear process for deciding who needs to know and what happens next?
The gap matters because digital and physical risk increasingly overlap. The Security Executive Council's executive targeting research found that 85 percent of the incidents it examined involved physical activity. Researchers also documented cyber incidents and cases where online activity and physical behavior converged.
A leadership team should be able to answer three questions:
Who monitors threats against the executive?
Who decides when something deserves a closer look or escalation?
How does that information reach physical security, legal counsel, law enforcement, or the executive's family when action is required?
A pile of alerts is not an executive protection program. Automated monitoring and AI can help teams identify more signals, faster. Someone still has to determine whether online threats against executives are from an account that is venting or escalating, whether an incident stands alone or fits a larger pattern, and whether the facts require action.
Technology helps you see more. Judgment tells you what deserves your attention.

What Can Someone Find About You and Your Family?
Online threats against executives go beyond the office. For many of them, far more personal information is available online than they realize.
In Nisos's 2026 Executive Digital Exposure research, 94 percent of the executives studied had a home address publicly linked to their name. Eighty-six percent had interior photographs, floor plans, or blueprints for a residence available online.
Every executive studied had breach data linking their name to at least one current email address. Sixty-four percent had a Social Security number exposed in breach data.
Then the circle widens.
Immediate family members maintained an average of eight public social media accounts. Nisos found that 97 percent of those accounts disclosed some personal information about the executive.
Thirty-two percent of executives or family members had shared their geolocation data via fitness apps or geotagged posts. Twenty-five percent of executives or their spouses had at least one public social media profile photo featuring a minor child.
None of those facts necessarily looks alarming on its own. Together, they can answer questions you would never intentionally answer for a stranger:
Where do you live?
Who lives there with you, and where do they spend time?
Where do you travel?
What does your daily routine look like?
A spouse's post can reveal travel. A child's sports photo can identify a school or team. A fitness app can expose a recurring route. An old real-estate listing can show a home's layout years after the sale.
The same online environment that harbors hostility toward a CEO can also reveal where that CEO lives, travels, and spends time with family.
Your family should not be discovering those exposures in the middle of an active threat. The time to find them is now.
What Should You Do When an Online Threat Targets Your CEO?
Preserve what you found, understand the broader pattern, assess the executive's exposure, and deliver the right information to those who may need to act.
Start with the evidence. Online content changes quickly. Posts are edited. Accounts disappear. Conversations move.
Capture what matters:
The post, account, date, time, and links
The surrounding conversation and relevant comments
Any references to the executive, family, home, travel, or upcoming events
Any signs the same person or group is escalating across platforms
Then widen the picture. Review the source's previous activity. Look for repeated focus on the executive, increasingly specific language, attempts to make direct contact, personal information, or growing interest in the executive's location and how they are protected.
At the same time, look at the executive's own exposure.If someone has shown hostile interest in a CEO, leadership should know how easily that person could obtain a home address, phone number, family relationships, travel patterns, personal email accounts, or images of the residence.
From there, the response should follow the evidence. Ask:
Does physical protection need to change?
Does additional evidence need to be preserved or investigated?
Does the executive or family need guidance?
Does the situation warrant involving law enforcement or emergency services?
The FBI's behavioral threat guidance underscores the importance of evaluating concerning behavior and CEO threats in context and identifying patterns that may indicate increasing risk.
A disciplined process protects leaders from two costly mistakes: dismissing a meaningful warning and treating every hostile comment as an imminent threat.
Most hostile speech will remain speech.
The goal is to recognize when the facts have changed enough to require action.

How to Reduce an Executive's Digital Exposure Before a Threat Appears
The safest time to discover that your home address is exposed online is before somebody hostile starts looking for it.
The same applies to a spouse's phone number, a child's public account, a recurring route, or an interior photograph of a residence.
Start by mapping the executive's digital footprint. Include immediate family members where appropriate. Identify what is visible, where it originated, and which information poses the greatest physical or digital risk.
Then reduce what you can:
Remove unnecessary personal information wherever possible.
Tighten privacy settings and close inactive accounts.
Submit and revisit data-broker removal requests.
Reduce unnecessary location sharing.
Review what family accounts reveal when viewed together.
Personal information resurfaces. New breaches, data brokers, and changing social accounts continually create exposure. A one-time cleanup is a snapshot. Ongoing monitoring helps prevent the footprint from quietly rebuilding.
Every piece of targeting information that is harder to find increases the effort required to reach the executive or their family.
Every concerning signal found early gives the team more time to understand CEO threats and act.
CEO Threats: What Executive Protection Looks Like Now
At Fortalice, we work from a simple premise: protecting a leader requires understanding the digital environment around them before it becomes an emergency.
That perspective is shaped by experience advising leaders in high-stakes environments, including founder Theresa Payton’s tenure as White House Chief Information Officer.
That means knowing what is being said, what personal information is exposed, which activity warrants closer scrutiny, and who needs to know when something changes.
Fortalice helps clients do that through Executive Digital Protection, including Digital Bodyguard™, Digital Footprint & Takedowns, and Threat Hunting. The work includes monitoring threats across the open, deep, and dark web, identifying exposed personal information, reducing unnecessary digital exposure, and investigating harassment or other concerning activity.
That work is human-driven for a reason. An alert can tell you that someone mentioned your name. An experienced analyst can assess who is talking, what else they have said, what information they may have found, whether their behavior is changing, and whether the people responsible for protecting the executive need to act.
That matters when the signal is ambiguous and the consequences are personal. If you are unsure what a stranger can learn about you or your family, find out while the answer is still useful, not urgent.
If you are unsure whether your organization would see an emerging online threat, ask who is monitoring today.
If something concerning has already appeared, take it seriously enough to understand it.
The goal is simple: see the risk earlier, understand what it means, and give yourself more time and options to respond.

About Fortalice Solutions
Fortalice is a cybersecurity firm specializing in cyber incident response, cyber risk management, and cybersecurity for executives, chosen by leaders who need elite, discreet support when cyber incidents threaten operations, reputation, and leadership credibility.
Founded by former White House CIO Theresa Payton, who served in a position defined by trust, discretion, and decision-making at the highest levels, Fortalice brings national-level experience and seasoned judgment to high-pressure, time-sensitive situations where decisions cannot wait and mistakes are costly.
The firm integrates cyber advisory, cyber incident response, technical testing, executive digital protection, and training into a unified approach shaped by real-world incidents and human decision-making, delivering clear, actionable guidance trusted by both executive leadership and security teams.
Connect with Fortalice to ensure trusted, discreet expertise is in place before, during, and after a cyber incident.

